A cross-chain bridge lets value move between blockchains that cannot communicate directly. It locks or destroys an asset on the source chain and issues a representation of it on the destination chain. That representation is a claim on the bridge, and its worth depends entirely on the bridge continuing to honour it.
Why blockchains cannot talk to each other
Each blockchain is a self-contained record. Its validators agree on its own state and have no way to observe any other chain, so a token on one network cannot simply be sent to another: the receiving network has no way of learning that anything happened elsewhere.
This is not an oversight. A blockchain's guarantees come from every participant verifying the same history. Accepting a statement about a different chain means accepting something the network cannot check for itself, and that is exactly where trust has to come back in.
So the phrase "moving a token across chains" describes an outcome, not a mechanism. Nothing crosses.
How a cross-chain bridge works
A cross-chain bridge works by holding or destroying an asset on one chain and issuing a matching token on the other, on the word of whoever it trusts to report what happened. There are three common designs.
Lock and mint. The asset is locked on the source chain and the same quantity of a new, "wrapped" token is issued on the destination chain. Going back, the wrapped token is destroyed and the original released. This is the most common design.
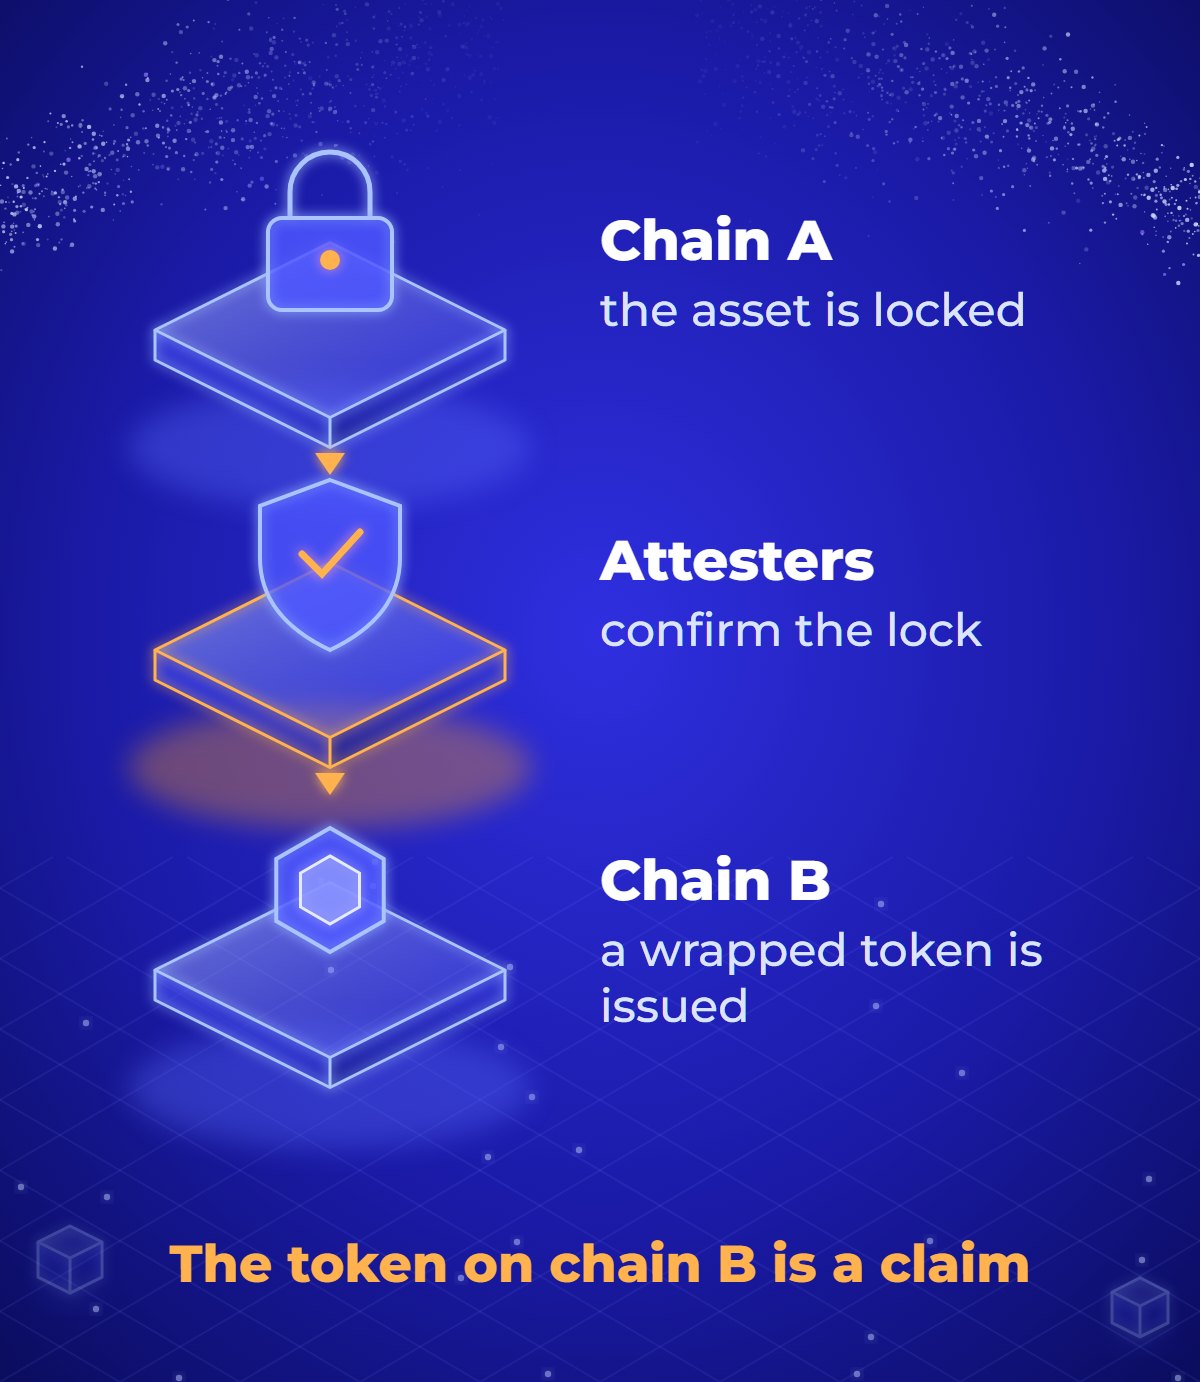
Lock and mint: the token on chain B is a claim on what is locked on chain A.
Burn and mint. The asset is destroyed on the source chain rather than held, and reissued on the destination chain. This only works when one issuer controls the asset on both chains.
Liquidity pools. Pools on both chains let a user deposit on one side and withdraw an asset already held on the other. No new token is created; the limit is whether the pool holds enough.
In every design someone has to confirm that the event on the source chain really happened: a set of validators, a multi-signature group, or a cryptographic proof checked by a contract. That set of parties, or that proof, is the bridge's security model. The chains on either side have generally kept working correctly through every major bridge failure; what failed was the part in between, which is why it pays to understand what a smart contract can and cannot guarantee.
How much has been stolen from bridges?
Bridges have lost about $3.7bn to attacks since 2021, and after two quiet years the losses have returned. In a Trusty Digital analysis of DefiLlama's public database of hacks, 96 incidents flagged as bridge attacks account for $3.69bn of the $21.07bn recorded across all incidents to 1 October 2026 (DefiLlama hacks database, downloaded 3 October 2026; amounts in US dollars at the time of each loss).
- 2021: 12 bridge incidents, $656m.
- 2022: 13 incidents, $1.91bn, 52% of all value stolen that year.
- 2023: 7 incidents, $301m.
- 2024: 7 incidents, $37m.
- 2025: 11 incidents, $38m.
- 2026 to 1 October: 46 incidents, $752m, 34% of all value stolen so far this year.
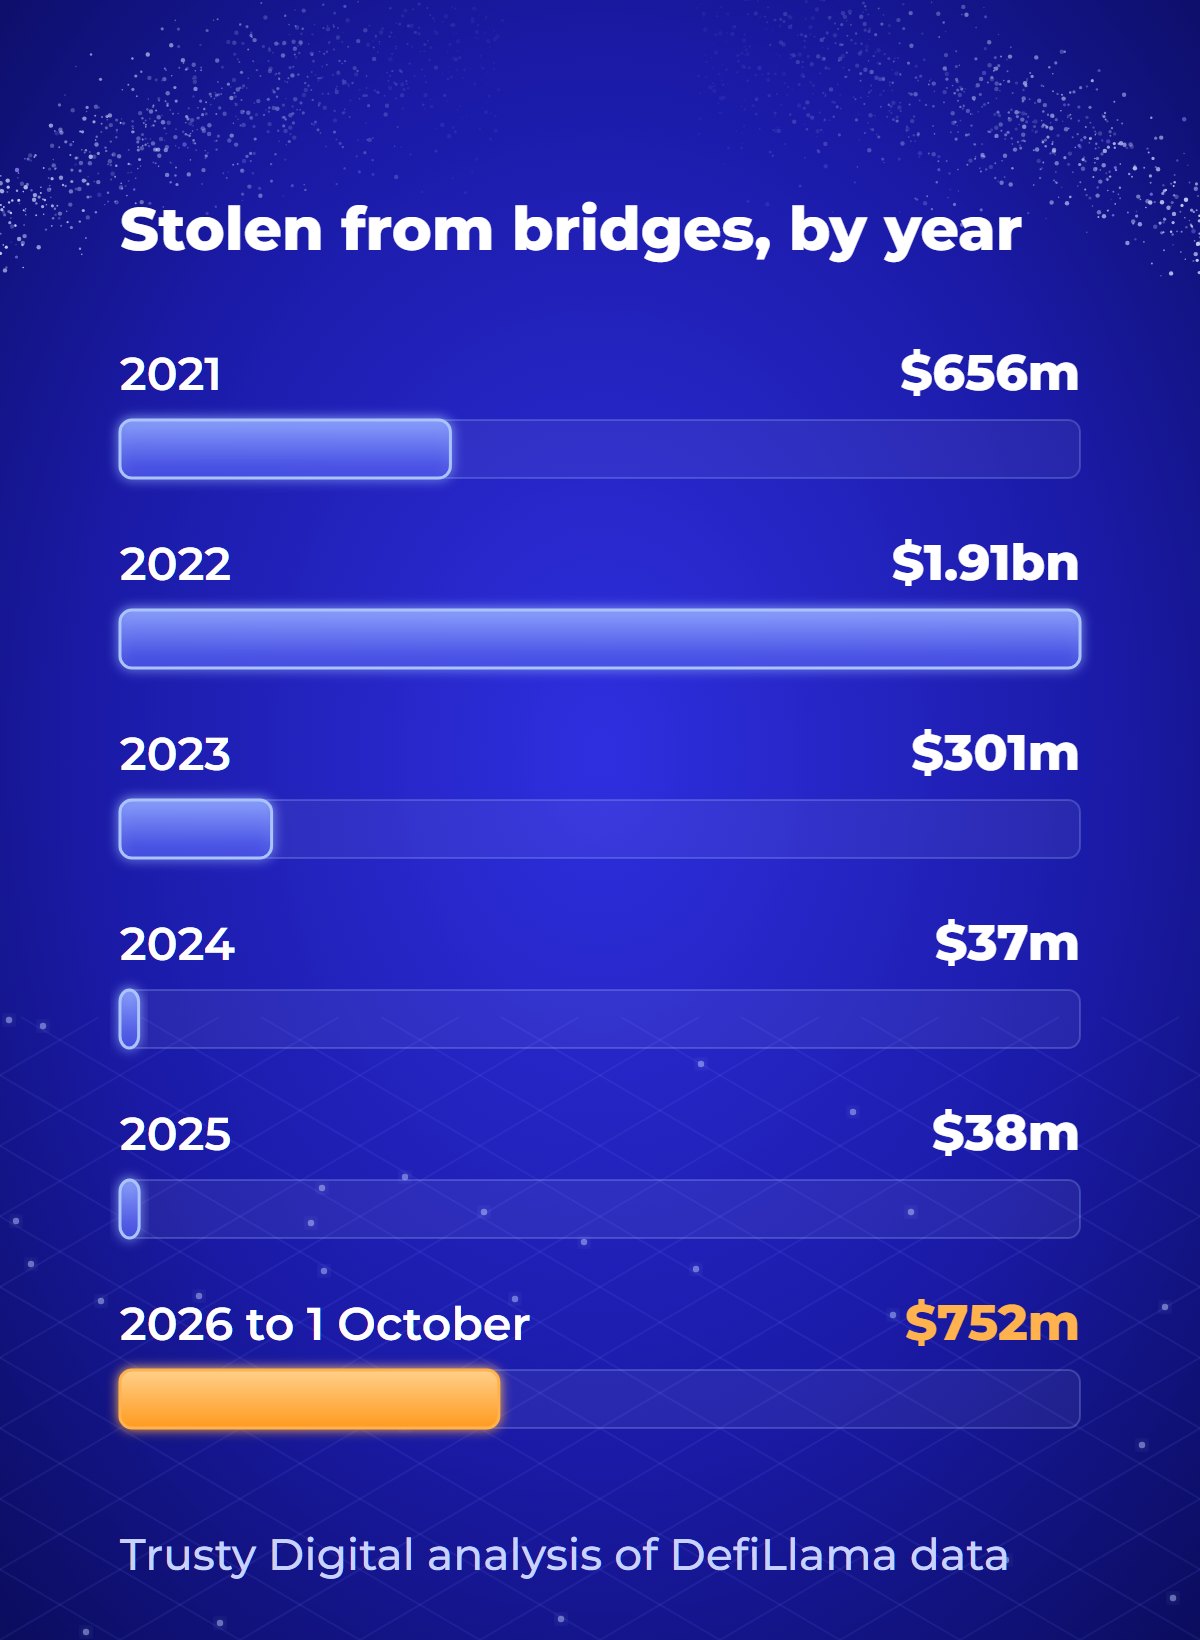
Value stolen from cross-chain bridges by year. Trusty Digital analysis of DefiLlama data, 3 October 2026.
The 2022 figure matches what Chainalysis reported at the time: about $2bn stolen across 13 bridge hacks, 69% of all funds stolen in 2022 up to August (Chainalysis, 2 August 2022). The largest single losses in DefiLlama's records are Ronin ($624m, March 2022), Poly Network ($611m, August 2021) and the Binance bridge ($570m, October 2022). Two of the six largest are from 2026: Kelp ($293m, April) and Liquid Network ($320m, September).
Trackers count differently, so treat any single figure as an estimate. The pattern is consistent across them: bridges are attacked less often than other targets, but when they fail, they fail big.
Why bridges are the target
Bridges are attacked because they concentrate value behind a mechanism that is weaker than the chains it connects. A lock-and-mint bridge holds the locked assets of everyone who has crossed it, in one place. Whoever can convince it that a deposit happened, or that a withdrawal is due, can take them.
The recorded failures follow from that. In DefiLlama's classification the most common causes of bridge losses are flaws in the bridge's own logic, forged proofs, tokens minted on one side with nothing locked on the other, and compromised validator or administrator keys. All of them sit in the layer that confirms events between chains, not in the chains themselves.
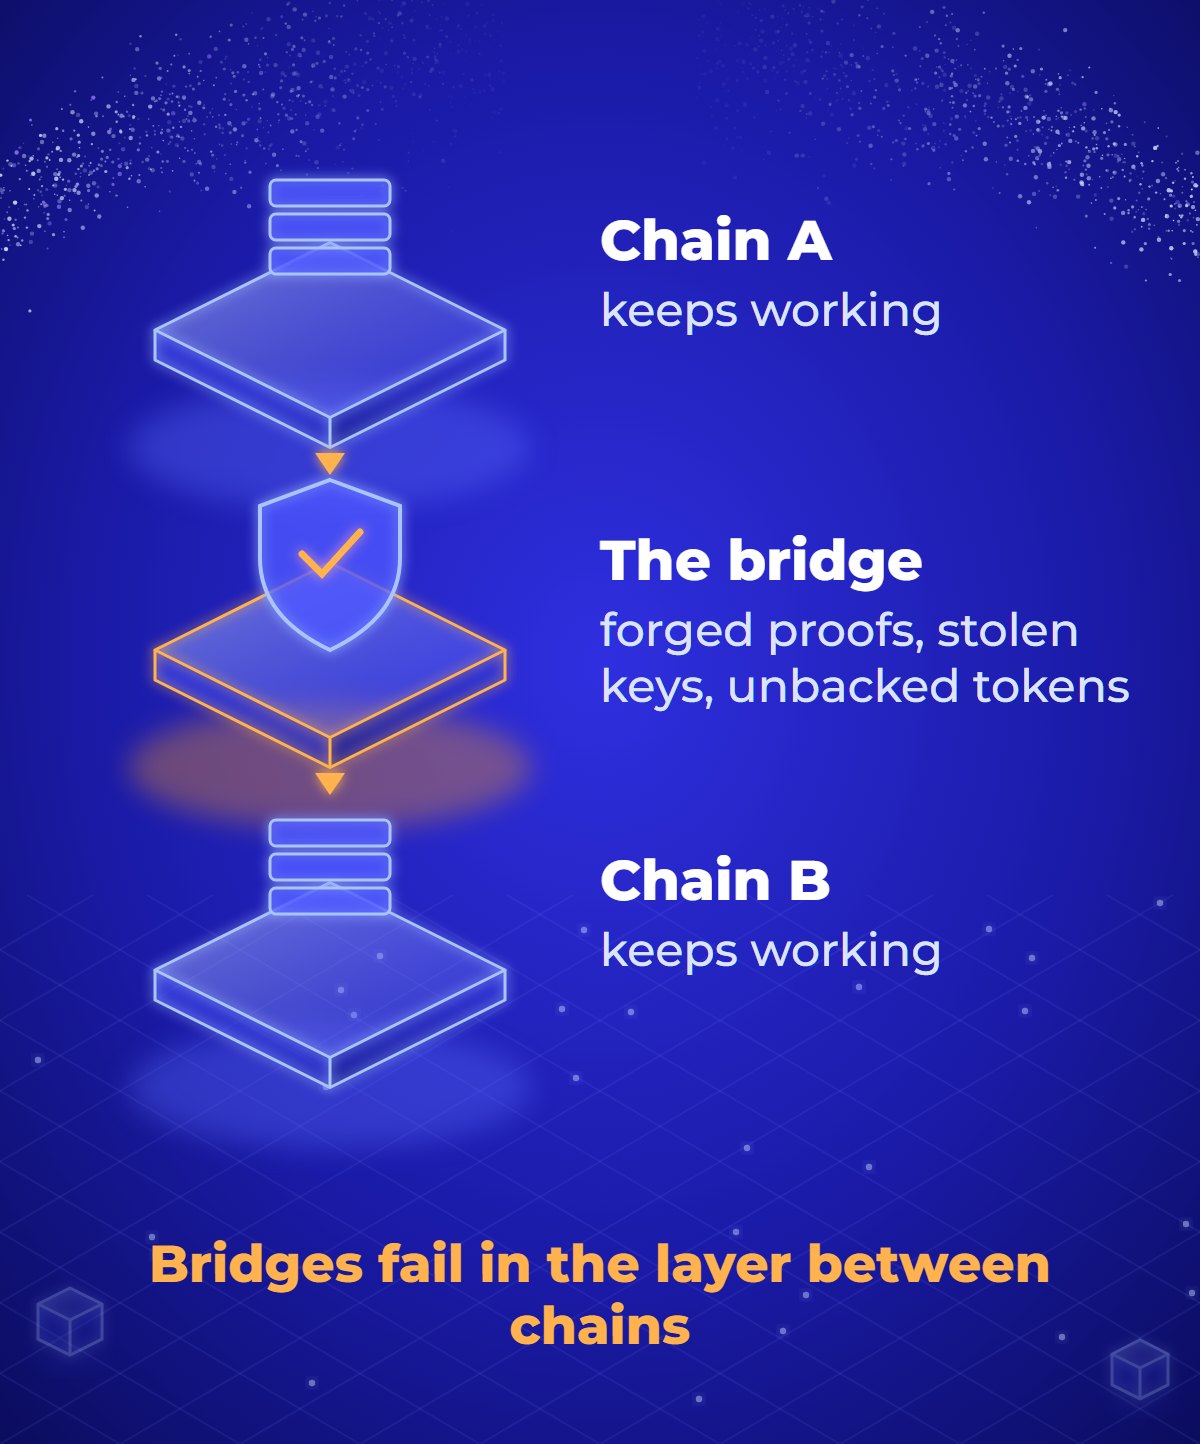
The chains keep working. Bridge failures happen in the layer between them.
The problem has not gone away. In 2026, 46 separate bridge incidents have been recorded so far, more than in the four previous years combined.
What you are holding after you bridge
A claim, not the asset.
The token you hold on the destination chain is a new token, issued by the bridge, whose value rests on the expectation that the bridge will release the original when asked. If the bridge is compromised and the locked assets are taken, the representation stays on the destination chain and is worth nothing. The chain will still report your balance accurately. The balance will simply be a record of a claim against something that is gone.
The safer alternative, where it exists, is an asset issued natively on the chain you use. Circle, for example, issues USDC directly on 38 blockchains, including Algorand, so a holder there holds the issuer's own token rather than a bridge's claim on it (Circle, Multichain USDC, checked 3 October 2026). Native and bridged versions of the same asset can carry the same name; the asset ID tells them apart.
For tokenised real-world assets the consequence is sharper. If a token represents an interest in a company and that token is bridged, what exists on the far side is a claim on a bridge that holds a token that represents an interest in a company. Whether the company's register recognises the holder on the far side is a question of company law, and the answer is often no. Before bridging an instrument, establish who the issuer treats as the holder, and see what a tokenised instrument actually is for why the register, not the ledger, governs.
Questions to ask about any bridge
Who confirms transfers, and how many of them are there? A threshold of five of nine known parties is a different proposition from two of three anonymous ones.
What happens if they disappear? Is there a way to recover the locked assets without them, or are they the only route?
How much is locked? The value held is the size of the prize. A bridge holding a large balance is under continuous, well-resourced attack.
Has the code been reviewed, by whom, and when? And has it changed since.
Who can upgrade it? A bridge that can be upgraded can be changed by whoever holds that power.
Is there a native version of the asset? If the issuer already issues it on the destination chain, you may not need the bridge at all.
What is the recourse if it fails? Usually none. It is better to know that in advance.
When you do not need a bridge
Most tokenisation programmes do not need one, and the cheapest way to manage bridge risk is not to take it.
An asset issued on one chain, held by holders on that chain, transferred on that chain and redeemed on that chain never meets a bridge. The pressure to bridge usually comes from wanting access to activity on another network. For a single-issuer instrument with restricted transfers, that is often not a real requirement on closer inspection. If holders need to arrive from elsewhere, the simpler pattern is to let them convert at the edge and hold the instrument natively on its own chain. The conversion risk is then a transaction they choose to make, not a permanent property of the instrument.
Trusty Digital issues on Algorand by default and does not operate a bridge. Where a programme genuinely needs to exist on several chains, that is a structural decision to take deliberately, with the questions above answered first.
Questions people also ask
Are cross-chain bridges safe? Some are better designed than others, but none is risk-free: every bridge adds a party or a proof system you have to trust, on top of the two chains. Bridges lost $752m to attacks in 2026 to 1 October, according to DefiLlama's records.
What is a wrapped token? A token issued on one chain to represent an asset locked on another. It is only as good as the bridge holding the original.
Is a bridge the same as an atomic transfer? No. An atomic transfer settles several transactions together on one blockchain, enforced by the protocol itself. A bridge connects two blockchains and depends on whoever confirms events between them.
The short version
A bridge does not move a token between chains. It locks an asset on one side and issues a claim on the other, and the claim is only as good as the parties or proofs the bridge relies on. That design concentrates value behind a mechanism weaker than the chains it joins, which is why bridges have lost about $3.7bn since 2021, and $752m in 2026 alone. Use a native asset where one exists, and bridge an instrument only after deciding, with the issuer, who the holder on the far side really is.
This article is general information, not legal, tax or investment advice.


 10 min read